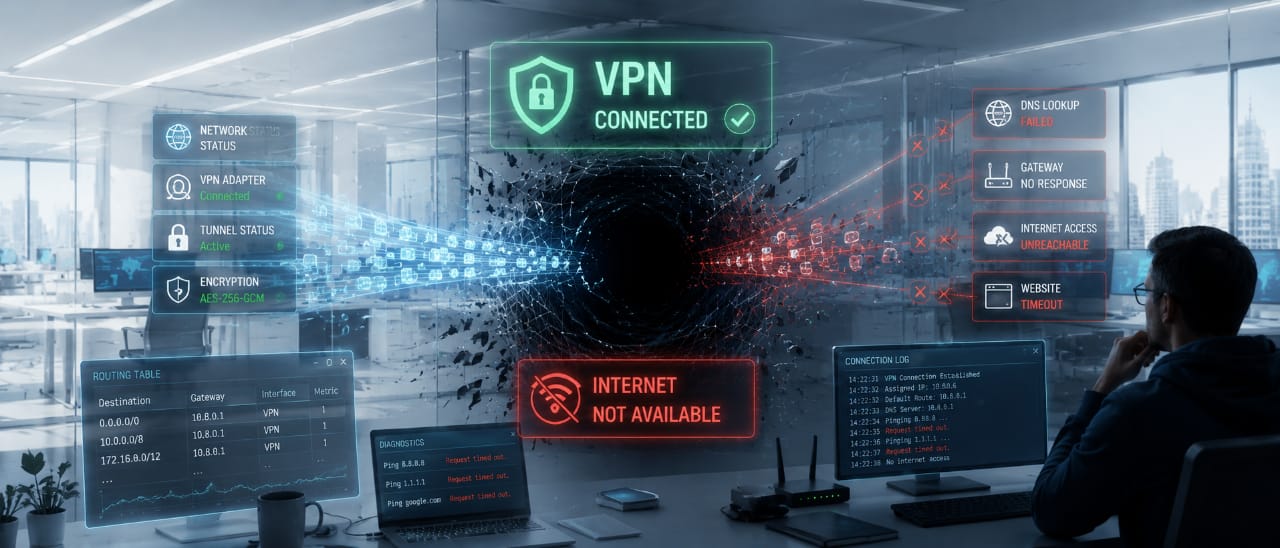
Every power user experimenting with network privacy eventually hits the exact same brick wall: you launch your secure tunnel, the client app turns bright green, but your PC’s internet connection instantly vanishes. Meanwhile, your smartphone—connected to the exact same home Wi-Fi network—is running perfectly.
Standard Google troubleshooting steps like "flush your DNS cache" or "reboot your PC" work less than 10% of the time. They are superficial fixes for a problem rooted deep inside the architecture of the Windows network stack and virtual interface routing conflicts.
Let’s dissect the three actual engineering reasons why Windows turns your active connection into a digital black hole, and look at how to fix it manually.
1. The Virtual Driver War and Gateway Metric Chaos
When you install a VPN client, Windows spawns a virtual network adapter—usually a TAP or TUN driver. This virtual card is designed to intercept your outbound data packets and force them through your encrypted pipeline.
The conflict begins if your machine has hosted other VPN providers, corporate remote-work clients, or custom proxy tools in the past.
Driver Overlap: Windows accumulates a messy backlog of legacy TAP network drivers. The operating system gets fundamentally confused about priorities.
Gateway Metric Glitch: Every network route in Windows has a "metric" value—the lower the metric, the higher the priority of that gateway. During a software conflict, Windows can accidentally assign your physical ISP router a higher priority than your secure virtual tunnel. Your OS then attempts to send raw, unencapsulated packets straight through your ISP link while the VPN client is trying to force encryption. The packets don't match the routing table, and your traffic drops into a void.
The Fix: Open Device Manager, expand Network Adapters, and ruthlessly uninstall every virtual driver labeled TAP, TUN, or Virtual except for the one tied to your active client framework.
2. Packet Splitting at the MTU Border (The Fragmentation Drop)
The Maximum Transmission Unit (MTU) defines the largest data packet size (in bytes) that can traverse a network interface without being split up. For standard US residential broadband, this default is 1500 bytes.
When you initialize a VPN, the cryptographic protocol encapsulates your data payload inside its own protective envelope. This process adds metadata headers to every single packet, expanding its physical size.
The Fragmentation Block: If an encapsulated packet exceeds the 1500-byte threshold, your router or your ISP's upstream gateway must fragment it into smaller pieces. However, if any hardware node down the pipeline enforces a strict "Don't Fragment" policy, your heavy, encrypted packets are immediately dropped by the carrier network.
Why Mobile Works: Mobile operating systems are natively engineered around volatile cellular bands and automatically lower their MTU boundaries out of the box. Windows, by default, stubbornly demands a full 1500-byte envelope.
The Fix: Go into your VPN client’s advanced settings and locate the MTU slider. Manually lower the threshold from 1500 down to 1350 or 1400. This shrinks the overall packet footprint, allowing your encrypted data to clear carrier gateways without triggering fragmentation drops.
3. The DNS Resolution Deadlock
To keep your browsing habits shielded from ISP tracking, a premium VPN client forces your system to drop your standard DNS servers and adopt secure, private resolvers hidden deep inside the encrypted tunnel. But the Windows core is notoriously sluggish when switching network states on the fly.
If your physical network card properties are hardcoded with static DNS IPs (like old Google or Cloudflare addresses), or if you run aggressive local filtering software, you create a routing deadlock. Windows attempts to resolve a domain name through your physical interface, which has already been isolated by your VPN client for security. Your browser returns a "Server Not Found" or timeout error, even though your direct IP connection to the VPN node is completely stable.
The Fix: Transition to clean, open-source clients that manage system DNS resolution directly at the kernel level (such as AmneziaVPN or custom upstream builds designed for VLESS/Xray). Under your physical network adapter settings, ensure that "Obtain DNS server address automatically" is checked, giving your secure tunnel total control over your routing tables.
Don't rely on the automated "troubleshoot connection" buttons built into bloated commercial VPN apps. Understanding the exact mechanics of how your data packets travel saves hours of configuration downtime and keeps your perimeter secure under any network conditions.
#CyberSecurity #WindowsNetworking #TAPAdapter #MTUBottleneck #DNSRouting #VLESS #XrayCore #SysadminTips #vpn-top-shop