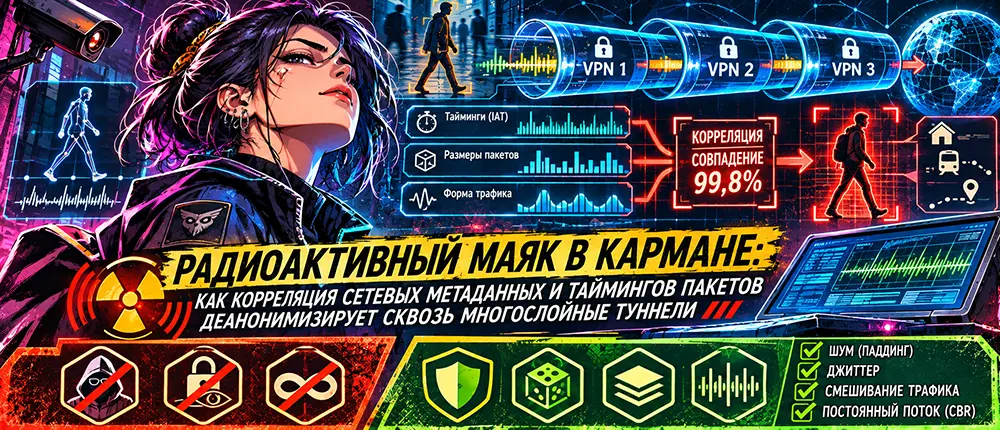
You step into a subway car at the terminal station. Your hood is pulled down over your brow, your face is covered by a mask, and your phone is turned off and tucked away in an inner pocket. You don't speak, you don't look at the cameras, and you are certain you have dissolved into the crowd.
Yet, a person with a stopwatch is following you. They don't need to see your face. They log the intervals between your steps, the duration of your stops, your walking speed, and the exact moment you pass through the turnstile.
At another station, a second observer records a similar sequence of events. The two logs are compared. Out of hundreds of passengers, only a few candidates remain, and additional observations gradually narrow the field.
The mask remains on. No documents are checked. But your route is already beginning to emerge from the anonymity.
This precise principle is the foundation of Traffic Correlation Attacks: methods that allow network flows to be linked via metadata without ever decrypting their payload.
You can use AES-256-GCM, ChaCha20-Poly1305, WireGuard, VLESS, or multi-layer routing. Cryptography will protect the payload. But it is not designed to hide transmission times, data volumes, and the sequence of network activity bursts.
And this is where things get truly interesting.
Stop right there. If you think that three proxies and the word ENCRYPTED automatically make you invisible, you might as well close this tab.
But if you want to understand how two observers at opposite ends of an encrypted route can link connections without a single stolen key, welcome to the network intelligence laboratory.
1. Correlation Architecture: When the Adversary Doesn't Break Encryption
Imagine an adversary capable of observing traffic near your device while simultaneously monitoring traffic near the exit node of an anonymizing network.
This could be a major network operator, a coalition of cooperating ISPs, research infrastructure, or an adversary controlling multiple routing vantage points.
They do not need to see the entire network. All they require are suitable observation points, precise timestamps, and a sufficient volume of data.
A simplified schematic:
[User]
      |
      v
[Observer A]
      |
      v
[Encrypted Tunnel]
      |
[Intermediate Nodes]
      |
      v
[Exit Server]
      |
      v
[Observer B]
      |
      v
[Target Resource]

A + B -> flow matching
       -> connection probability estimation
The first observer sees when the user sends data and when responses arrive. The second records similar bursts of activity near the exit node.
The system compares time series, transfer volumes, and flow directions. When a sufficiently distinct signature appears, it can detect a statistical correlation.
This is not an AES crack. It is a way to bypass the need to crack it.
However, an important engineering nuance: correlation is not automatic proof of identity. Its accuracy depends on background traffic, the number of concurrent connections, measurement precision, and the adversary's capabilities.
Inter-Arrival Times: The Digital Pulse of a Connection
Inter-Arrival Time (IAT) describes the intervals between the arrival of consecutive packets.
A modern web page does not load in a single continuous stream. The browser requests HTML, then fetches assets, executes scripts, establishes auxiliary connections, and receives responses.
An activity pattern emerges: short bursts of packets, pauses, and new surges.
This pattern can partially persist even after encryption and traversal through intermediate nodes.
However, it is not replicated perfectly.
Router queues, congestion, retransmissions, multiplexing, varying packet sizes, and network jitter distort the original sequence.
Consequently, a serious correlator does not look for an absolute match between two charts. It evaluates statistical dependence while accounting for delays and noise.
One of the fundamental tools is the Pearson correlation coefficient:
[
r=\frac{\operatorname{cov}(X,Y)}{\sigma_X\sigma_Y}
]
Yet, a high coefficient by itself does not prove that two streams belong to the same user. Correct temporal synchronization, false-positive control, and verification against independent data are required.
This is why impressive figures like "99.8% de-anonymization" prove nothing when presented without a description of the experiment.
2. Packet Size: When Encryption Leaves a Silhouette
Encryption hides the contents of a message, but the length of the transmitted blocks frequently remains observable.
The tunnel adds its own headers, control fields, and cryptographic overhead. Fragmentation, MTU, aggregation, and transport specifics can alter the sizes of external packets.
Nevertheless, the distribution of lengths and transfer directions can contain clues about the nature of the activity.
This is the premise behind Website Fingerprinting research.
The analyzer receives a sequence of observable characteristics:
- packet or record sizes;
- transfer directions;
- intervals between events;
- volumes of individual bursts;
- session duration and structure.
Next, a statistical model or neural network attempts to determine which website or type of activity corresponds to the observed pattern.
This does not mean any website can be identified from fifty packets with guaranteed accuracy. The results heavily depend on the website corpus, the adversary model, background load, and applied defenses.
Yet, the sheer possibility of classifying encrypted traffic is an established field of research.
And the uncomfortable takeaway is obvious: an encrypted stream may reveal more about your behavior than the padlock icon in your browser suggests.
3. Flow Watermarking: When the Adversary Leaves a Temporal Tag
Passive analysis observes an already existing traffic pattern.
Active watermarking goes a step further.
If an adversary controls a suitable network segment, they are potentially capable of modifying the temporal transmission structure by introducing minor delays or modulating the sequence of events.
Another observer then attempts to detect this structure after the traffic has passed through the tunnel.
If the watermark survives intermediate nodes and is reliably recognized, it provides additional evidence linking the streams.
Yet, this is not a magical DPI button.
Success depends on observation duration, route stability, network noise, the level of control available to the adversary, and the chosen watermarking technique.
The attack may yield false positives or lose the signal entirely.
Even so, the principle is deeply unsettling: the adversary attempts to turn packet delivery timing into an invisible connection signature.
4. Why Multi-Layer Tunnels Do Not Guarantee Anonymity
Multi-hop routing divides knowledge about a connection among multiple nodes.
This is a significant advantage.
If one server sees the user but doesn't know the final destination, and another knows the destination but cannot see the original user, establishing a link becomes much harder.
However, the model shifts when an adversary can simultaneously observe matching segments of incoming and outgoing traffic.
In such a scenario, they can attempt to match their statistical characteristics.
Tor
Tor is designed with anonymity in mind, but flow correlation remains a major threat against a sufficiently strong adversary.
At the same time, claiming that "Tor is useless" would be technically incorrect. The network substantially complicates observation and connection-linking compared to direct access.
WireGuard
WireGuard primarily solves the problem of secure network tunneling.
Its architecture focuses on cryptographic protection and efficiency rather than the guaranteed elimination of temporal activity fingerprints.
Therefore, expecting it to possess the properties of a full-fledged anonymizing network is incorrect.
VLESS and XTLS Vision
Vision mechanisms are tailored for specific traffic processing and masking tasks, including aspects of TLS interaction.
However, Vision is not a universal defense system against end-to-end traffic correlation.
It does not guarantee the elimination of temporal regularities between the entry and exit points of a connection.
It is important not to confuse protocol-detection resistance with resistance to user activity correlation.
These are entirely different tasks and threat models.
5. Engineering Defense Protocols: What Actually Reduces Metadata Leaks
Rule number one: absolute invisibility cannot be promised.
Instead, the engineer defines the adversary's capabilities and evaluates which connection characteristics they are capable of observing.
Padding: Obscuring Exact Lengths
Additional data can reduce the informational value of transmitted message sizes.
However, various approaches exist: fixed sizes, sets of permissible sizes, adaptive padding, and other schemes.
Each comes with a cost: increased traffic volume, latency, and resource overhead.
Furthermore, padding does not automatically eliminate temporal regularities.
Traffic Shaping: Altering the Rhythm
Managing queues, speeds, and dispatch times allows you to modify the observed flow structure.
However, random delay by itself does not guarantee protection.
For instance, the command:
tc qdisc add dev eth0 root netem \
  delay 15ms 5ms distribution normal
can be used in a controlled lab environment to simulate latency.
Yet, it is not a proven method for destroying correlation. It alters network characteristics and may degrade application performance.
Crucially, random jitter does not necessarily destroy persistent regularities across large time windows.
Cover Traffic: Filling the Silence
Background dummy traffic can mask certain periods of real activity.
However, random packet dispatch and Constant Bitrate Shaping are not the same thing.
To approximate a constant observed stream, the system must manage transmission rates independently of current user load, injecting dummy data as needed.
This is expensive.
Continuous transmission increases bandwidth costs, power consumption, and infrastructure strain. And if actual load exceeds the configured profile, queues and delays may occur.
Even this setup does not guarantee protection against all observation methods: the characteristics of connection initiation and termination, transfer directions, and application interactions still persist.
Route Splitting
Using different network paths and operators can complicate observation for an adversary with limited coverage.
Yet, asymmetric traffic routing by itself does not guarantee anonymity.
If the adversary controls the necessary points on both routes, correlation remains feasible.
Moreover, complex routing increases operational risks and requires separate fault-tolerance verification.
6. What to Audit in Real Infrastructure
For a rigorous privacy assessment, it is not enough to spin up a VPN, look at a new IP address, and declare victory.
Laboratory testing against a predefined adversary model is required.
One must evaluate what information is available to an observer across different network segments, how size and time distributions change, how many false positives the correlator produces, and how robust the results are under realistic background loads.
Crucially, three distinct objectives must not be conflated:
Confidentiality: Can an outsider read the transmitted data?
Protocol Masking: Can an observer determine which transport or tunnel is in use?
Anonymity: Can an observer link a user to a specific action or resource?
A single tool does not have to solve all three tasks.
Conflating these concepts is precisely what breeds a dangerous illusion of security.
Conclusion: Encryption Does Not Hide Your Shadow
Imagine an armored steel door. The lock cannot be picked, the key exists only with you, and the contents of the room are securely protected.
Yet, a narrow sliver of light remains underneath the door.
The observer cannot see what is happening inside. Instead, they notice when you enter, how much time you spend in the room, and when you turn off the light.
They did not pick the lock.
They studied your shadow.
Modern network intelligence increasingly relies on these indirect indicators. Defeating cryptography is unnecessary if you can analyze the metadata surrounding it.
Therefore, true privacy does not begin with promises of "military-grade encryption," but with an understanding of what information an ideally encrypted channel continues to reveal.
Encryption protects the content.
But invisibility is an entirely different engineering challenge.