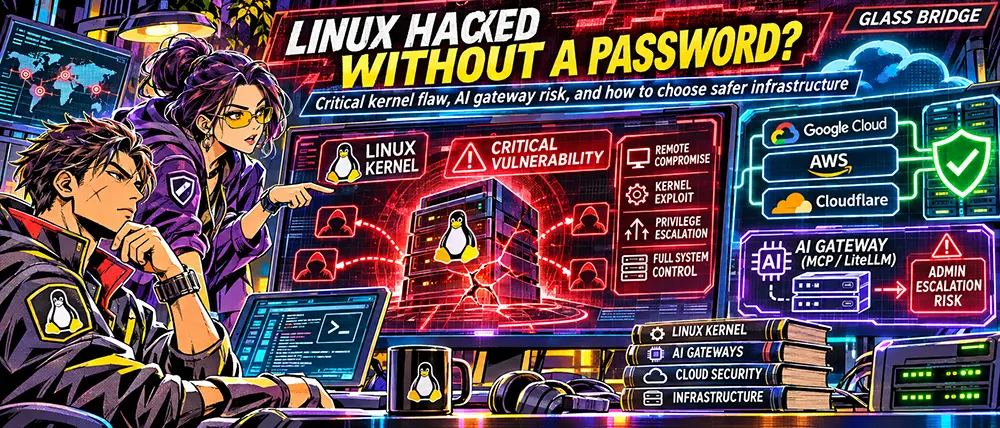
A critical Linux vulnerability has shown that even a strong password does not always save a server. We break down what happened, why AI systems are at risk, and whether Google Cloud, Amazon AWS, and Cloudflare are truly worth trusting.
In October 2026, security specialists discovered a dangerous bug in the Linux kernel. The vulnerability, designated CVE-2026-98432, received a severity score of 9.8 out of 10.
Researchers demonstrated the ability to gain full, remote control over a server. No password, no authorization, and no action required from the owner whatsoever.
Under certain conditions, a specially crafted network connection is all it takes.
How Can a Server Be Hacked Without a Password?
Every time a user opens a website or connects to a network service, the server processes incoming connections.
Linux was found to contain a memory management bug during the processing of TCP requests. Under specific timing conditions, the system could release a memory region that was still actively in use by another connection-handling process.
This type of flaw is known as a use-after-free vulnerability.
The consequences can range from a server crash to arbitrary code execution.
On October 27, researchers at Anthropic reported the creation of an exploit that grants root privileges on a Linux server running an exposed MPTCP service.
Root access provides virtually complete administrative control over the operating system.
Important: researchers demonstrated a successful breach under specific conditions. This does not mean that every Linux server can be guaranteed compromised with a single network packet.
However, the bug itself affects standard TCP processing, not just MPTCP. The vulnerable code had existed in Linux since version 4.4.
Adding to the concern, Go version 1.24 and later can automatically enable MPTCP for Linux listening sockets. Administrators might not even realize their application is utilizing this mechanism.
Why Does This Matter for VPNs?
Most VPN servers operate on Linux. Modern encryption protects transmitted data, but it does not patch operating system bugs.
If an attacker gains root privileges on the server itself, they can potentially access configurations, keys, and data accessible to that system.
Therefore, the reliability of a VPN depends not only on the chosen protocol, but also on the security of the underlying server infrastructure.
Another Danger: When an AI User Becomes an Administrator
During the same period, information was published regarding vulnerability CVE-2026-114612 in LiteLLM—a software gateway designed to interface with various neural networks.
In vulnerable versions, a single cryptographic system was used both to protect secrets and to verify authorization tokens.
Under certain conditions, a user with limited internal privileges could forge an administrative session and gain the ability to execute commands on the server via MCP.
This is not a mass compromise of ChatGPT or Claude users. We are talking about specific server software and particular preliminary attacker privileges.
However, the takeaway is crucial: even a secured operating system will not save you if an application improperly segregates access rights.
Google Cloud, Amazon, or Microsoft: Whom Should You Trust with Your Server?
Following incidents like these, a natural question arises: where should you host your website, VPN, or AI service to ensure maximum security?
Google Cloud is one of the strongest contenders.
Google boasts a global network infrastructure, while Cloud Armor provides defense against various types of DDoS attacks. Basic network security mechanisms operate automatically, and advanced capabilities help counter more complex threats.
Amazon AWS is an equally serious competitor.
AWS Shield Standard is automatically available to Amazon clients and protects against common network DDoS attacks. Additional scenarios are covered by advanced tools, including Shield Advanced and AWS WAF.
There is also a third major player—Microsoft Azure, which offers its own network security, monitoring, and DDoS mitigation mechanisms.
It is impossible to name a single absolute winner. Every provider has strengths, and actual resilience depends on the architecture and configuration of a specific project.
For a VPN, server protection and power are not the only priorities; connection latency, IP address availability, outbound traffic costs, and the ability to quickly failover to a backup node are equally important.
Where Does Cloudflare Fit In?
Cloudflare deserves separate consideration.
For standard websites, its proxying allows you to filter malicious requests, withstand DDoS attacks, and hide the origin IP address of your server, provided the infrastructure is configured correctly.
However, standard Cloudflare website protection does not automatically secure arbitrary VPN protocols.
Specialized products exist for certain TCP/UDP services—such as Cloudflare Spectrum—but their capabilities and availability depend on your pricing plan and protocol.
Why Even Google Cloud Doesn't Guarantee Protection Against This Linux Bug
This is where a fundamental distinction lies.
A DDoS attack and the exploitation of a kernel vulnerability are completely different threats.
During a DDoS attack, an attacker attempts to overwhelm a server with a high volume of requests. Network defense systems can detect such traffic and rate-limit it.
When exploiting CVE-2026-98432, a relatively small amount of specially crafted network traffic can be enough to pose a danger.
Even if a virtual server is hosted on Google Cloud or AWS, its underlying operating system still requires security updates.
The cloud provider secures its own infrastructure and supplies defense tools. However, the administrator of a standard virtual machine remains responsible for the state of the Linux running inside it.
What Should Server Owners Do?
First—check your installed kernel using the command uname -r and cross-reference it with your distribution's security bulletin.
Second—check the status of MPTCP using the command sysctl net.mptcp.enabled.
Third—install kernel patches and reboot the server. Temporarily disabling MPTCP may mitigate certain risks, but it does not eliminate the underlying bug.
Fourth—close unnecessary public ports, restrict administrative access, and set up monitoring and backups.
Finally, provision a backup server with the same or a different provider. The failure of a single node should not halt your entire service.
So Which Servers Are the Best?
When it comes to serious cloud infrastructure, Google Cloud, Amazon AWS, and Microsoft Azure rightfully rank among the top candidates.
For projects focused on VPNs and network services, Google Cloud can serve as an excellent foundation, AWS as a strong alternative, and Cloudflare as an additional layer of website protection.
However, the best server is not necessarily the most expensive one, nor does it necessarily belong to the largest company.
It is a server that remains accessible to your users, receives timely updates, is protected against network attacks, features redundancy, and allows for rapid recovery after an outage.
The Linux and LiteLLM vulnerabilities have clearly demonstrated that even the most powerful infrastructure remains vulnerable if you neglect any single layer of its security.
Glass Bridge | November 4, 2026
Sources: Linux Kernel CNA, Akamai Security Intelligence Group, AWS Security Bulletin 2026-160, GitHub Security Advisory GHSA-7hp6-4w63-5g45, Google Cloud Armor documentation, AWS Shield, Microsoft Azure, and Cloudflare.