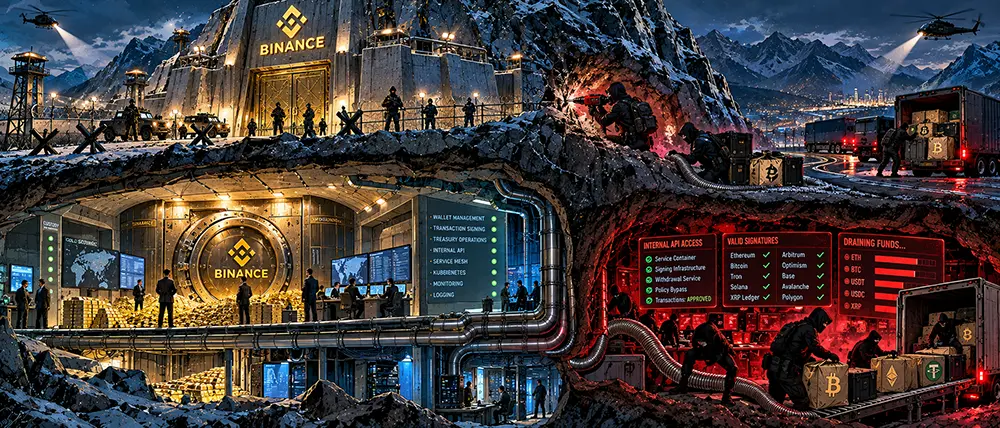
Imagine a Swiss bank carved straight into solid rock.
At the entrance stand anti-tank hedgehogs. The gates are made of a meter of solid titanium. Inside, you have motion sensors, biometrics, armed guards, and a vault that cannot be opened with a single key. For years, the bank showcases this fortress in commercial ads so that depositors can sleep soundly at night.
But a bank has to operate.
That is why on the side of the cliff, there is a small service door. Through it pass engineers, couriers, the accounting department, service teams, and thousands of internal orders: transferring funds, confirming payments, updating balances, opening locks.
And one night, the attackers do not even approach the titanium gates.
They gain access to the service corridor.
And then the worst thing happens.
The vault isn't cracked open.
The vault receives a properly formatted order and hands over the money on its own.
This is precisely why what happened on October 29, 2026, with Binance is far more interesting than yet another story about "hackers stealing cryptocurrency."
According to Binance's own estimate, the scale of the incident reached approximately $6.3 billion. The company reported that roughly $3 billion was successfully frozen, and losses will be covered by SAFU and internal funds. Binance’s preliminary investigation points to a potential compromise of a DevOps engineer's laptop, after which the attacker gained access to a service container and was able to send unauthorized withdrawal requests. At the same time, Binance specifically emphasizes that no evidence of private key leaks has been found so far.
Official Binance security incident announcement
And that final phrase is far scarier than the first ones.
Because if the private keys truly were not stolen, another question arises:
who signed the transactions then?
For those who just want to understand what happened
Imagine a company director's electronic signature.
The thief didn't steal the signature itself or learn how to forge it. They breached the internal accounting system and somehow forced the legitimate corporate mechanism to sign their payment orders.
At the exit, the bank sees a real document.
The signature is real.
The format is real.
The system says: everything is fine.
Only the money goes to the criminal.
This is precisely the picture blockchain forensics is revealing right now.
TRM Labs tracked approximately $6.36 billion leaving Binance-linked wallets across ten blockchains simultaneously. The bulk of the assets was moved in about twenty minutes. Ethereum, Bitcoin, Tron, XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche, Polygon. This was not a single forgotten wallet or a single strange smart contract.
Chainalysis independently reported to Reuters that by 00:30 GMT, its specialists confirmed the theft of at least $5.912 billion. At that time, Chainalysis had not yet definitively confirmed the exact attack vector.
In terms of scale, this is the largest known crypto heist in history. The previous staggering record held by Bybit in February 2025 was around $1.5 billion.
And now, the most important part.
Bitcoin was not hacked. Ethereum was not hacked. Cryptography was not defeated.
The systems received valid signatures and executed the commands.
If this explanation is enough for you, you can close the article.
Seriously.
Go back to scrolling TikTok, looking at cute cats, and arguing about where Bitcoin will go tomorrow. For the average user, the main takeaway has already been delivered: the world's largest crypto exchange took a hit of roughly $6.3 billion, not because someone mathematically "broke the blockchain."
Next up will be EIP-7702, nonces, signing infrastructure, trust boundaries, and a very uncomfortable question about what the word "secure" actually means in a modern distributed system.
Engineers may stay.
Part II. The fortress wasn't breached. It opened the gates itself
The most interesting piece of evidence appeared on Ethereum.
In May 2025, alongside the Pectra upgrade, Ethereum introduced the EIP-7702 mechanism. It allows a standard Externally Owned Account to temporarily acquire programmable behavior through smart contract execution delegation.
EIP-7702 is not a vulnerability in itself.
It is a standard Ethereum feature.
According to the official specification, an authorization contains, among other things, a chain ID, the delegated code address, a nonce, and a cryptographic signature from the account owner. Once correctly authorized, account calls can execute the code of the specified contract.
Official Ethereum EIP-7702 Specification
And this is where the beauty of the engineering nightmare begins.
According to TRM Labs, the attacker obtained 50 signed EIP-7702 authorizations for sequential nonces of the Binance hot wallet in advance.
Why fifty?
Because a hot wallet is active. It constantly processes transactions, and its nonce changes.
Instead of trying to guess a single state, the attacker had a series of pre-signed authorizations. When the transaction hit the network, one of them matched the active nonce.
That turned out to be enough.
At 20:20 UTC, the Binance wallet was delegated to a sweeper contract controlled by the attack operator.
Just 3 minutes and 24 seconds after delegation, a single operation drained 167,464 ETH along with 63 other tokens, including approximately 1.615 billion USDT. The delegation remained active, and incoming funds later on were systematically drained as well.
If the story ended here, everything could be written off as an Ethereum-specific quirk.
It didn't end there.
Ten blockchains break the simple version of the attack
Almost simultaneously, funds began leaving Binance wallets on other networks.
And there was no EIP-7702 involved there.
Bitcoin uses a different model.
XRP Ledger uses another.
Tron uses another.
Solana uses another.
Yet Binance-linked wallets kept generating validly signed transactions favoring a single attacker control loop.
TRM therefore draws a critical conclusion: most likely, the attacker managed to force Binance's hot-wallet signing infrastructure to sign transactions of their choosing across multiple networks simultaneously. Binance has not yet published the final root cause.
This is where the story about the "infected laptop" ends.
Or rather, the laptop remains important, but its role changes.
The compromise of a DevOps engineer's laptop can easily explain the initial access.
It still does not explain something else:
why did the compromise of a single workstation make it possible to reach a trusted perimeter capable of authorizing the withdrawal of billions of dollars across multiple blockchains?
These are fundamentally different questions.
Getting into a bank and being able to order the vault to hand over gold should not share the exact same access level.
Part III. Now clear children from the monitor: architecture time
A modern crypto exchange does not store billions of dollars in a wallet.dat file on an administrator's laptop.
Between the user who clicked Withdraw and the actual blockchain transaction lies a long chain of trust.
The frontend accepts the request.
The identity system identifies the user.
The risk engine evaluates the operation.
The withdrawal service builds the transaction.
The policy layer checks limits, addresses, networks, and context.
The signing infrastructure generates the cryptographic signature.
The broadcast service sends the result to the blockchain.
In a normal architecture, the compromise of a single element in this chain should not automatically mean the compromise of the rest.
This is where the main engineering hypothesis of this investigation emerges.
We do not yet know whether attackers stole IAM credentials, workload identity, internal API tokens, access to signing orchestration, or compromised another control plane component. Binance has not yet published a technical post-mortem.
Therefore, claiming that "hackers stole the Vault master token," "broke MPC," or "seized the Kubernetes control plane" would be pure journalistic fantasy right now.
However, the blockchain leaves us with a much firmer piece of evidence:
someone obtained valid Binance signatures for operations Binance never intended to execute.
And not just on a single network.
This is no longer a hypothesis about a virus on a laptop. It is an observable consequence of how the system behaved.
Why MPC and HSM are not a magic shield here
Following attacks like this, a question almost inevitably arises:
"Don't major exchanges use HSMs, multisigs, and MPC?"
They do use complex security systems.
Yet herein lies one of the most unpleasant conceptual flaws in modern cybersecurity.
Protecting a key and protecting the decision to sign a transaction are two entirely different tasks.
You can build an HSM from which it is physically impossible to extract a private key.
You can split a secret across multiple MPC nodes so that the full key never exists in a single place at all.
You can implement magnificent cryptography.
But if a trusted orchestration layer tells these components:
This transaction is approved. Sign it.
and the verification policy deems the request legitimate, the cryptographic system will honestly do its job.
It wasn't hacked.
It was used correctly for the wrong purpose.
This is a fundamentally different class of catastrophe.
Zero Trust that stopped right at the signer's door
NIST formulated the Zero Trust principle very simply: no user or resource should be automatically trusted simply because they reside "inside" a corporate network or belong to the organization. Authorization must be built around the specific user, device, resource, and action.
NIST SP 800-207: Zero Trust Architecture
Yet financial infrastructure demands an even stricter version of this principle.
It is not enough to ask:
"Does this service have the right to talk to the signing system?"
You must ask:
"Does this service have the right to sign *this specific transaction*, for *this specific amount*, on *this specific network*, to *this specific address*, right now, and after *this exact sequence of events*?"
That is no longer authentication.
That is semantic authorization.
And judging by the observable outcome of the attack, this is precisely where Binance's primary lesson lies.
Fifty signatures that should have lit the entire datacenter red
The most alarming detail of TRM's investigation isn't even the $6.3 billion.
It is the fifty pre-prepared EIP-7702 authorizations.
For a regular user wallet, EIP-7702 can be a useful account abstraction tool.
For an exchange treasury or hot-wallet infrastructure, an unexpected series of such authorizations should look roughly like a bank employee walking in at three in the morning with fifty pre-signed orders:
"If the vault is currently in state #18,914,775 — transfer control to this person. If it's already #18,914,776 — use the next document..."
This is not a routine transaction.
This is a modification of the account management model.
TRM explicitly recommends that treasury teams monitor EIP-7702 delegation, block such authorizations via policy unless expected, treat a series of authorizations for a nonce range as an indicator of compromise, and separate signing infrastructure and approval paths across networks and wallet tiers.
This is no longer theory.
These are recommendations from a forensic team following the largest crypto heist in history.
Where security actually broke
In my view, Binance's main lesson is not that "you cannot trust employees," "you shouldn't use hot wallets," or "EIP-7702 is dangerous."
Those conclusions are far too simplistic.
The model of transitive trust itself broke.
If a workstation trusts a service container, the container trusts the withdrawal service, the withdrawal service trusts the policy engine, and the policy engine is able to convince the signing infrastructure that an operation is legitimate, the attacker doesn't need to break the final bastion.
It is enough to capture a segment of the chain after which the system will continue trusting itself.
In the old security model, you protected the key.
In the new model, you will have to protect intent.
The signing system of the future must understand not only:
signature authorized
but also:
why this operation exists.
A multi-billion-dollar withdrawal should not become permissible simply because the request came from a properly authenticated service.
What is needed are independent policy domains, strict blast-radius limits, separation of wallets by network and function, distinct approval planes, behavioral volume controls, transaction simulation, destination policies, independent circuit breakers, and the ability to automatically halt signing infrastructure upon abnormal wallet behavior.
The keyword here is: independent.
If the same control plane simultaneously builds a transaction, confirms its validity, and obtains a signature, no amount of glossy green Security Certified badges will save the architecture from the compromise of that control plane.
The North Korean connection
TRM Labs links the operation with high confidence to TraderTraitor, a North Korean state-backed hacking cluster. The company points to on-chain and off-chain intelligence, preliminary preparation of the operation, the use of Tornado Cash to fund the operator wallet, infrastructure testing prior to the attack, and pre-obtained signatures.
This is currently an attribution by blockchain intelligence rather than a published final conclusion by law enforcement regarding Binance.
Yet the name TraderTraitor did not appear yesterday.
In February 2025, the FBI officially blamed North Korea for the theft of approximately $1.5 billion from Bybit and explicitly used the name TraderTraitor for this activity.
FBI: TraderTraitor and the 2025 Bybit hack
If Binance's attribution is confirmed, we are no longer looking at a series of random cryptocurrency heists.
This is an industrial model of state-sponsored cyber operations targeting financial infrastructure.
The most uncomfortable paradox of the whole story
Roughly half of the stolen funds were halted not thanks to the blockchain.
But thanks to centralization.
Tether managed to freeze USDT.
Circle blocked USDC.
Ripple froze a portion of RLUSD.
World Liberty Financial blocked USD1.
The Arbitrum Security Council exercised emergency powers.
According to TRM's early estimates, this stopped around $2.7 billion, while Binance later reported roughly $3 billion in frozen assets.
And this creates a magnificent philosophical paradox for the cryptocurrency world.
Centralization created a gigantic single point of risk concentration.
Yet when that point collapsed, another form of centralization helped recover some of the money.
USDT can be frozen precisely because an issuer exists.
Bitcoin cannot be frozen precisely because no such issuer exists.
Decentralization is simultaneously a protection and a problem.
Centralization is simultaneously a problem and an emergency brake.
What comes next
Following Binance, the industry will almost certainly begin revising not just how keys are stored, but the architecture of signature authorization.
HSMs are here to stay.
MPC is here to stay.
Cold storage is here to stay.
Yet the mere statement that "private keys were not leaked" is no longer enough.
Because the largest crypto heist can happen without anyone ever having to take a private key out of a secure vault.
The next generation of financial security will be built around a single question:
who, why, and under what circumstances has the power to make a key sign a specific action?
And that means shifting from Key Security to Intent Security.
Moving from protecting a secret to protecting a decision.
Moving from "we trust the internal service" to "we do not trust even our own service until a specific operation proves its legitimacy."
And here, old-school Zero Trust will finally have to be carried through to its logical conclusion.
Do not trust the user.
Do not trust the device.
Do not trust the network.
Do not trust the container.
Do not trust the API.
And most importantly:
do not even trust a valid cryptographic signature until you understand why the system decided to create it.
The 21st-century fortress
Binance's investigation is still ongoing. A full technical post-mortem is not yet available, so it is premature to definitively claim a specific initial-access chain or internal compromise scheme.
This is precisely why today it is vital not to turn the investigation into conspiracy theories.
We don't need them.
The facts look terrifying enough on their own.
Roughly $6.3 billion in impact.
Ten blockchains.
Dozens of wallets.
Valid signatures.
Fifty pre-signed EIP-7702 authorizations.
About twenty minutes for the main phase.
And the world's largest crypto exchange, which has not yet found evidence of private key leakage.
The old banking fortress was built around the vault.
The digital fortress was built around the cryptographic key.
Yet it turned out that the 21st-century thief might not touch the vault at all.
They sneak into the control room.
Change the route.
Hand over the right command.
And the system opens the door itself.
Cryptography wasn't broken.
The fortress signed the heist itself.
Sources and technical references
Binance: Official Security Incident Update from October 30, 2026
TRM Labs: Complete on-chain breakdown of the $6.36B attack
Reuters: Chainalysis assessments and industry expert reactions
Ethereum Improvement Proposals: Official EIP-7702 specification