October 31, 2026 | Network Security, Node.js, Cloud Infrastructure
Imagine a warehouse where thousands of trucks arrive every day.
Each one brings tightly packed boxes. Staff unpack the goods, sort them, and send them on their way.
One day, a completely normal-looking box arrives. But inside is a cleverly designed mechanism that breaks the sorting machine the moment it is unpacked.
Security checked the truck. The documents turned out to be authentic. The box passed all checkpoints.
The problem only arose at the moment of unpacking.
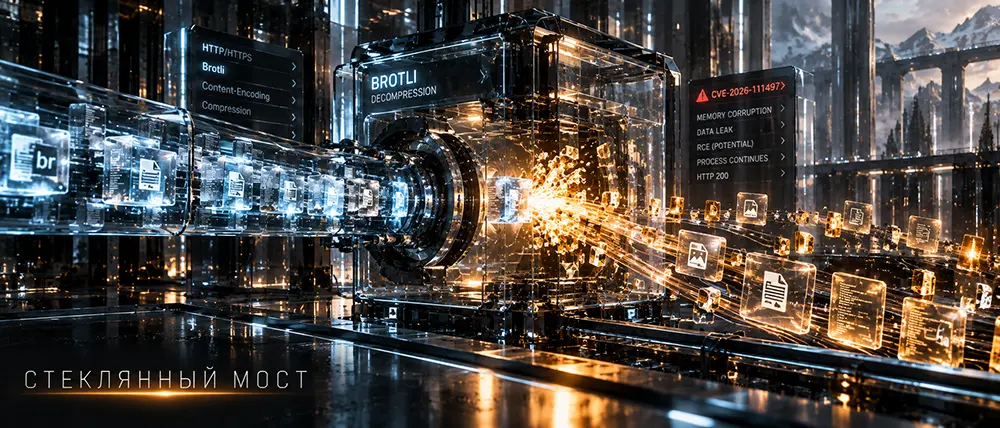
This is roughly how a new critical vulnerability in the Brotli library, discovered in October 2026, works.
Why the Internet Loves Compression
When we open a website, the browser needs to receive HTML, CSS, JavaScript, and other data.
To transfer them faster and save traffic, the server can compress the information before sending it.
At the other end of the connection, a special program restores the original content.
Brotli, developed by Google, has become one of the most common methods for this kind of compression.
It is precisely in this data restoration program—the decoder—that researchers discovered a dangerous flaw.
Eight Bytes That Can Create a Huge Problem
The vulnerability received the identifier CVE-2026-111497.
In certain situations, the decoder incorrectly distinguished between two things: corrupted data and data for which it simply needed to wait for the next portion.
Instead of stopping the processing of the invalid stream, the program continued to accept new bytes.
The internal buffer was designed for only eight bytes. But under certain conditions, additional data could be written to it.
This data spilled over into adjacent memory areas.
In programming, this is known as a buffer overflow.
The consequences depend on the specific environment: a program crash, memory disclosure, or, under additional conditions, the execution of arbitrary code.
The Strangest Part: The Server Might Keep Running
On October 29, specialists at Datadog Security Labs published the results of their own testing.
They reproduced the error on a vulnerable version of Node.js and verified that the patched version rejects the exact same corrupted stream.
However, another feature surprised the researchers.
In one of the tests, the server did not crash. It continued to respond to requests and even returned a normal, successful HTTP response.
At the same time, memory may have already been corrupted.
This creates an unpleasant situation: the monitoring system reports that everything is working, even though a violation has occurred inside the application.
This does not mean that every successful connection hides an attack, but it shows why monitoring HTTP statuses alone is not enough to detect such errors.
Why a Defensive Gateway Won't Always Help
Usually, an application sits behind Nginx, Cloudflare, or another protective layer.
It checks requests, limits suspicious activity, and blocks known attacks.
But there is an important nuance here.
The application itself can make requests to external websites and receive compressed responses from them.
For example, a user submits a link, and the server downloads the page to display its title and image.
If an external resource is controlled by an attacker, they can potentially return a specially crafted Brotli stream.
And then the dangerous data will be unpacked directly inside the application.
A standard incoming WAF will not necessarily see this exchange because the server is acting as a client itself.
The Vulnerability Travels Between Technologies
At first, the issue gained prominence because of Node.js.
However, Brotli is used much more widely.
Researchers found that affected implementations were also present in Python, Bun, .NET, Envoy, and Istio.
This is a critical point for modern infrastructure.
A developer might not even know that their application uses a specific compression library.
It can reside inside another package, an HTTP client, a container, or a network gateway.
Therefore, updating one program does not always fix the problem across all dependencies.
How This Relates to VPNs
It cannot be said that the Brotli bug automatically allows a VPN tunnel to be hacked.
Protocols like VLESS, VMess, and other transports do not become vulnerable simply due to this publication.
However, a VPN service consists of more than just transport.
There are control panels, APIs, web interfaces, logging systems, statistics, and automated deployment systems.
If one of these components processes untrusted compressed data through a vulnerable library, it may be at risk regardless of the tunnel's encryption strength.
This means that it is necessary to protect not only the data transmission channel, but the entire software environment surrounding it.
What Developers Should Do
The first rule is simple: update affected runtimes and libraries to patched versions.
The second: find out which components actually unpack data coming from external sources.
The third: separately check outgoing HTTP requests from the application, especially if a user can specify an address from which the server automatically retrieves information.
Temporarily disabling Brotli processing for untrusted data can reduce the attack surface, but it does not replace a proper fix.
And finally, it is essential to remember containers and built-in dependencies. Sometimes updating the system library does not help because an old copy is already bundled directly into the application.
Instead of a Conclusion
The Brotli story shows that danger can hide in completely ordinary technologies.
Not in a complex authorization system. Not in cryptography. Not in artificial intelligence.
Instead, in a program that simply unpacks data.
We are used to thinking about information security during transmission.
Yet what happens to that information after it is received is just as important.
Because even a perfectly secured channel will not save a server if the received data breaks it from the inside.
GLASS BRIDGE
Source material: official Node.js security advisory from October 21, Canadian Centre for Cyber Security warning from October 28, and reproducible Datadog research from October 29.
Wednesday, October 21, 2026 Security Releases+2