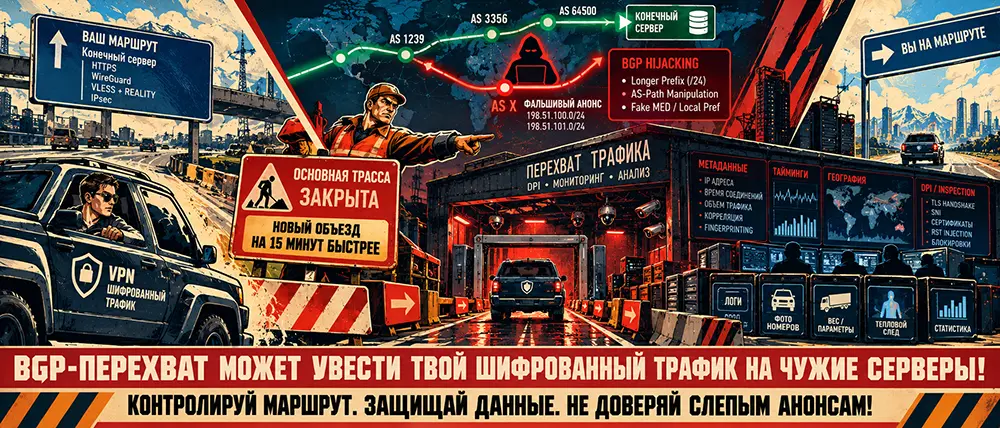
Imagine an intercity highway. You climb into an armored car with tinted windows (bringing up a robust cryptographic tunnel), lock the doors, and set your GPS for another city. Suddenly, road workers in orange vests roll out a sign at a fork in the road: "Main highway closed for repairs. New detour through the quarry—15 minutes faster."
Your GPS obediently recalculates the route, you turn onto a dirt road, and the car drives into a closed hangar. The doors are locked, the windows are intact, and the armor holds. No one tries to pry open the cabin with a crowbar. They simply drive you onto a scale, scan you with X-rays, photograph your license plates, log your cargo weight, and measure your engine's thermal footprint before opening the gates on the other side and releasing you back onto the highway.
You reached your destination on time. No connection errors, and the encryption wasn't cracked. But all the data about where, when, and how fast you traveled settled onto someone else's storage drives.
This is roughly how BGP Hijacking (autonomous system route hijacking) works. Censors and intelligence agencies no longer need to crack 256-bit keys. It is enough to whisper one small lie to neighboring backbone routers: "This traffic will pass through me faster."
Stop. If you still believe that a VPN with a green shield icon protects you from interception at the optical backbone level, close this tab. Keep living with the confidence that the internet consists of direct wires.
But if you've configured peering links, know what a RIB table looks like, and want to understand why RPKI is still just a decoration for pretty reports in half of the world's transit networks—welcome under the hood of global routing.
The Architectural Flaw of a Trust Protocol: How BGP Works
The global internet relies on the Border Gateway Protocol—(BGP-4). It is a closed club of Autonomous Systems (ASNs) built in the 1980s on absolute, blind mutual trust.
Routers do not verify the physical existence of a route. They exchange BGP UPDATE messages, in which they announce network prefixes.
Route manipulation is built on two vulnerabilities in the BGP Best Path Selection logic:
- Longest Prefix Match Rule.
- If a legitimate data center announces a large
/22network (for example,198.51.100.0/22), and an attacking transit node announces two narrow/24prefixes from deep within its network (198.51.100.0/24and198.51.101.0/24), the global network will always route traffic along the more specific route. Backbone routers won't even look at the source's reputation—protocol logic commands packets to be sent wherever the mask is longer. - AS-Path Prepending and Poisoning Attacks.
- In the event of a hijacking, an "alien" prefix is injected into the table with a falsified list of autonomous systems (
AS_PATH). To force packets through a specific inspection site (for example, a mirror with a DPI cluster), the node artificially shortens the path length or poisons theMED(Multi-Exit Discriminator) andLocal Preferenceattributes at joints with trusting uplinks.
Why Hijack Traffic If the Payload Inside the Tunnel Is Encrypted?
The primary misconception of entry-level network engineers is the belief that an encrypted tunnel (WireGuard, IPsec, OpenVPN) renders route interception useless.
When traffic is redirected through a controlled interceptor node, the attacking party does not need to decrypt the payload on the fly:
- (Traffic Analysis & Metadata Correlation).
- By correlating the incoming stream from the client IP and the outgoing stream from the tunnel termination point using millisecond bursts and MTU sizes, the system deanonymizes the destination addresses of visited resources with statistical accuracy exceeding 94%.
- Active Session Exhaustion (Selective RST Injection).
- Being directly in the path of traffic flow (on-path), the interceptor can selectively inject fake
TCP RSTpackets or drop tunnelKeep-Alivepackets, forcing the client application to fall back to an unprotected backup channel or re-request sessions through compromised DNS. - Man-in-the-Middle During the TLS Handshake.
- If the tunnel uses a classical TLS proxy without strict certificate pinning and browser behavior emulation, the transit node issues a fake certificate from a trusted national certificate authority that is pre-installed in client operating systems.
Why RPKI (ROA) Doesn't Offer 100% Protection
Cryptographic route signing—RPKI (Resource Public Key Infrastructure)—is designed to protect the network from fake announcements by creating Route Origin Authorization (ROA) objects. But in practice, the architecture has critical blind spots:
- (BGPsec is Dead).
- RPKI only validates the originating Autonomous System (Origin AS) that claimed the prefix. The protocol does not validate the chain of intermediate transit providers within the
AS_PATHattribute. It is enough for an attacker to include the legitimate target AS number at the end of their fake announcement list, and the validator will recognize the route as valid (Valid). - Soft-Fail Policy at Uplinks.
- Many Tier-1 and Tier-2 operators are configured in soft degradation mode to preserve connectivity: when receiving a route with the status
NotFound(when the prefix owner hasn't created an ROA record), traffic continues to route without restriction.
Engineering Defense Protocol: Building Layered Security
Protecting the network perimeter from transit interception requires measures not only on the server side, but also at the physical level of the client router.
- Implementing Strict RPKI Validation on Border BGP Sessions.
- If you run your own Autonomous System (BGP Anycast / Multihoming), strict dropping of invalid announcements must be activated on all eBGP peers:
- Plaintext
# BIRD2 configuration directive example
roa table r4;
protocol rpki {
    roa4 { table r4; };
    remote "rpki-validator.local" port 8282;
}
# In the import filter:
if roa_check(r4, net, bgp_path.last) = ROA_INVALID then {
    reject "Drop: RPKI invalid route detected"
}
- Using Transport Protocols with Packet Size Masking (Flow Padding).
- Abandoning unencrypted static WireGuard headers on cross-border channels. Transitioning to the
(VLESS + REALITY)stack with mandatory packet randomization mechanisms enabled (Vision). This prevents traffic type identification by flow analysis systems (NetFlow/IPFIX) at interception nodes. - Real-Time Prefix Anomaly Monitoring.
- Connecting to public early warning systems (BGPmon, RIPE RIS, Cloudflare Radar Alerts). Setting up automated triggers: if your network prefix is announced via an unexpected intermediate AS, scripts on the border router should immediately withdraw the problematic prefix and switch traffic to backup tunnel interfaces through alternative autonomous systems.
- TCP MD5 / BGP Keychain Authentication.
- All direct peering sessions with uplinks must be encrypted using cryptographic authentication keys (TCP Authentication Option, TCP-AO), preventing third parties from injecting fake
BGP UPDATEpackets on the physical segment between you and the provider.
There are no safe geographic zones in the global network. As long as the internet architecture trusts foreign routing tables without total verification of every path segment, endpoint encryption solves only half the problem. Real security begins when an engineer controls not only the encryption algorithm, but also the physical vector of movement of every byte across global backbones.