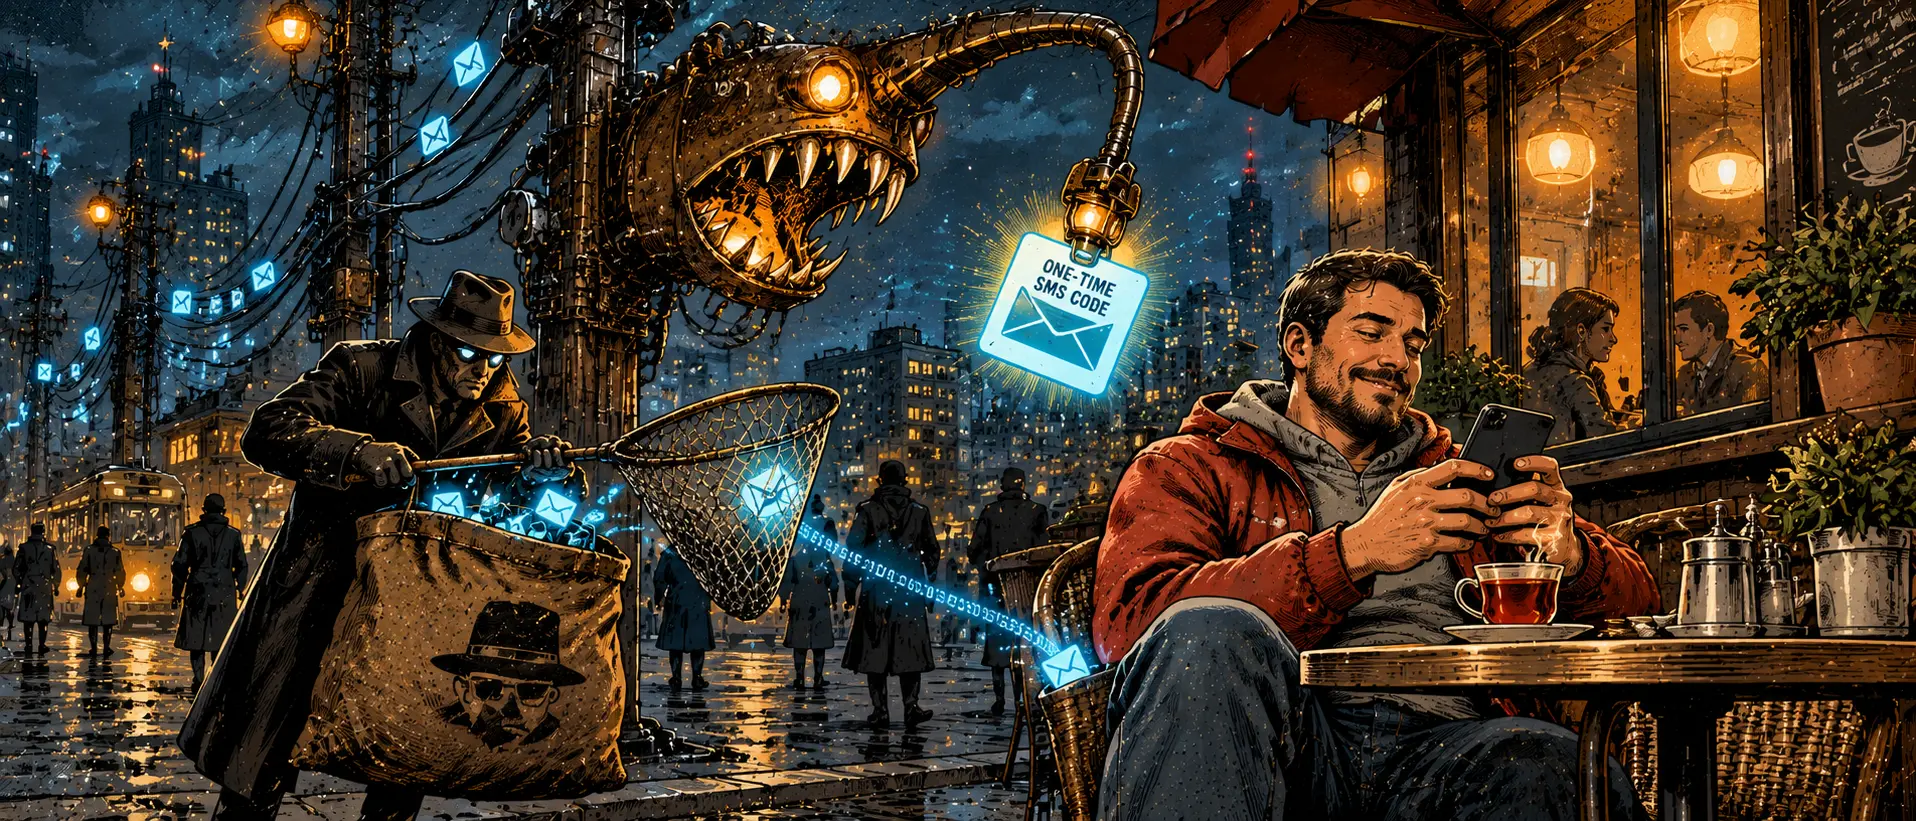
Last time we dove deep into network engineering to figure out why DoH and DoT protocols expose provider routing through unmasked SNI. Today, strictly following our alternating schedule of "engineering vs. everyday pain," we are coming back down to earth.
Let's talk about the foundation that 99% of our accounts, online banking portals, and private chats still rely on: one-time SMS codes.
Here is a skin-crawling scenario: you are quietly sipping your morning coffee, your phone is lying face down on the table, no notifications. Ten minutes later, an email hits your inbox: “A login to your account from a new device was detected, your password was successfully changed.” You grab your phone—and it suddenly displays "No service" or just stays silent while money drains from your account.
You didn't click any links or download any viruses. You were simply erased from the cellular network behind your back.
Anatomy of a betrayal: how the code flies past your screen
Most people believe that SMS is a direct and secure line between their bank and their SIM card. In reality, cellular networks were designed in the last century without anticipating that million-dollar transactions would be authorized through them.
Your code gets intercepted via three well-established paths:
Fake power of attorney and SIM-swapping. The dirtiest yet most effective social engineering method. A straw man walks into a mobile store in a residential neighborhood with a crudely printed power of attorney or simply finds a corrupt employee for a cut of the profits. Within two minutes, the operator issues a duplicate of your SIM card. Your original card instantly dies ("No service"), and all bank SMS, Telegram, and WhatsApp codes start pouring into someone else's phone.
A hole in the SS7 (Signaling System 7) protocol. The international signaling system connecting mobile operators worldwide is essentially built on absolute trust. Having access to an SS7 node (illegally rented through developing country operators), an attacker can command an operator to redirect incoming SMS for a specific number to their own virtual terminal. You won't even notice the signal dropping—the code is simply duplicated elsewhere.
Leaks from messaging aggregators. Banks and services don't send SMS directly from cell towers, but rather through bulk SMS providers and routing hubs. The servers of these intermediaries are often secured worse than a rustic fence. Fresh data dumps show that databases containing live streams of authorization messages periodically leak in real time.
The million-dollar fact: SMS was never a security tool
Why do financial giants and government portals still force this ancient tech on us?
Because it is cheap and covers 100% of basic push-button phones. Forcing everyone to adopt a secure hardware key or code generator requires billions in tech support and user training. Statistically, it is easier for banks to write off fraud losses as a cost of card maintenance than to break familiar user habits.
Within a cellular data packet, SMS is transmitted over the service signaling channel in virtually plain text. To a base station, your confirmation code for a 500,000-tenge transfer looks identical to spam about "shoe discounts."
Network self-defense: kicking the stool out from under hackers
Waiting for mobile operators to clean up their branches is a dead end. You need to secure your own perimeter:
Ban third-party actions via power of attorney with your carrier. Today, open your mobile operator's app (or visit an office with your passport) and file an official request: "Prohibit any registration actions and SIM card re-issuance via power of attorney." SIM replacements should only be done by you in person, looking an employee in the eye.
Total elimination of SMS from two-factor authentication. Wherever a service allows you to unbind your phone — unbind it immediately. Switch logins to TOTP generators (Aegis, 2FAS, Bitwarden) that generate one-time 6-digit codes locally on your processor without touching the cellular network. Even if your SIM card is cloned, your account cannot be accessed without the local key.
Cloud password in Telegram and WhatsApp. If an attacker intercepts your SMS, they will hijack your messenger in one click unless two-step verification is enabled (an extra password known only to you). Turn it on right now—it takes three clicks in the privacy settings.
True cybersecurity begins the moment you stop trusting your mobile operator to decide whether it's really you or a stranger with a fake piece of paper.