October 27, 2026 | Editorial Analysis
We are accustomed to believing that an encrypted connection hides everything happening inside it from prying eyes.
However, a vast difference exists between protecting content and keeping the connection itself invisible.
In the summer of 2026, a group of researchers from Paderborn University presented a paper that offers a new perspective on Russia's internet filtering infrastructure.
It turns out that selective QUIC blocking mechanisms appeared in Russia significantly earlier than international research literature had previously assumed.
And the most intriguing aspect here is not political, but technical.
What QUIC Hides and What Remains Visible
QUIC is utilized, notably, by the HTTP/3 protocol. It combines secure data transmission with the ability to establish connections faster and maintain them when network routes change.
However, initial QUIC packets have a distinct characteristic.
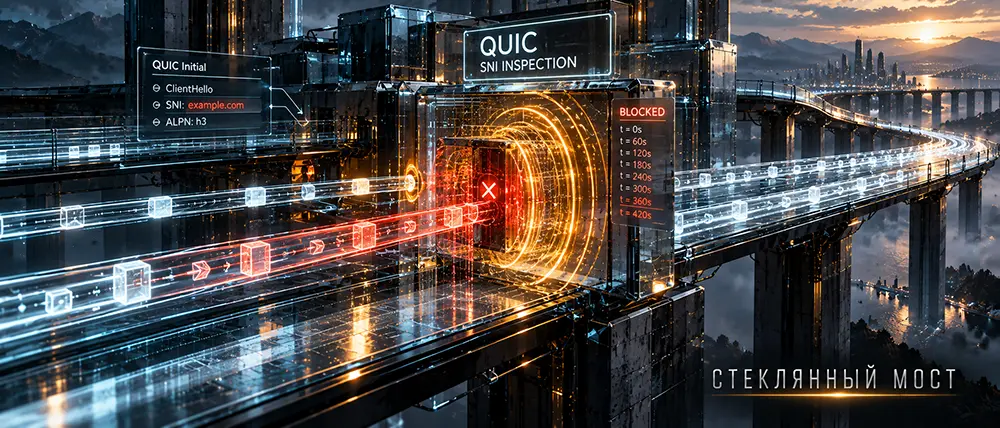
They are protected by keys that can be derived from publicly available connection parameters. Consequently, an observer is capable of decrypting initial QUIC Initial messages and extracting the TLS ClientHello from them.
If the ClientHello contains a plaintext SNI, the domain the client intends to connect to becomes exposed.
Meanwhile, the content of subsequent protected transmissions remains inaccessible without the corresponding secrets.
This creates a paradox: the protocol protects transmitted data, but its initial phase may reveal enough information to make a blocking decision.
From Blunt Blocking to Targeted Analysis
In early 2022, Russian networks began widely restricting international QUIC traffic.
The initial system recognized characteristic initial packets and could block the entire corresponding flow.
However, the researchers reconstructed the timeline and established that a transition to more selective filtering occurred between May 2022 and July 2023.
The system was now able to analyze the domain inside the QUIC Initial and block the connection based on the SNI.
The authors determined that a similar mechanism appeared in Russia at least nine months earlier than the widely documented deployment of an analogous system by China's Great Firewall.
This does not prove technology transfer between the countries or the existence of a shared developer. It merely establishes the timeline of deploying similar methods, as observed by researchers.
Seven Minutes After a Single Packet
One of the most interesting findings emerged in March and April 2026.
Researchers sent test QUIC packets from Moscow, Saint Petersburg, and Novosibirsk to a controlled server in Germany.
They discovered a stateful residual blocking mechanism.
If a packet triggered the filter, subsequent packets sharing the same combination of IP addresses and ports could be dropped for up to 420 seconds.
Furthermore, new packets could restart this timer.
This means the issue extended beyond merely dropping the initial connection.
The system maintained state and continued to block the traffic flow after the initial detection of a forbidden signature.
For diagnostic purposes, this is extraordinarily important.
A repeated connection attempt a few seconds later might not yield fresh information about server availability, as it could encounter an already active filter state.
Why Changing Ports Is No Longer a Universal Solution
The researchers uncovered yet another feature.
Early versions of QUIC filtering were predominantly tied to UDP port 443.
Yet, in measurements taken in 2026, filtering operated on other ports as well, including non-standard ones.
In Saint Petersburg and Novosibirsk, it affected all tested destination ports. In Moscow, isolated exceptions were observed among system ports.
This implies that simply changing the port number can no longer be considered a reliable, universal strategy.
If the filter recognizes the structure of the protocol itself, altering the external address parameter does not necessarily change the outcome.
An Unexpected Result with QUIC v2
At the same time, the researchers discovered a limitation within the filtering system itself.
In their experiments, QUIC version 1 was subjected to selective blocking, whereas standardized QUIC v2 was not blocked by the same mechanism.
This is an important technical finding, but it should not be turned into a marketing promise.
The research does not prove that QUIC v2 is always accessible in Russia, that any VPN built on it will function, or that filtering will remain unchanged following the publication of these results.
It merely demonstrates a specific incompleteness in the analyzer's implementation within the measured networks at the time of testing.
Such gaps can vanish following hardware and software updates.
What This Changes for VPN Engineering
The main lesson of the study is the necessity of separating several different causes of network failure.
A connection may fail due to an unreachable IP address, domain blocking, transport protocol characteristics, routing issues, or the persistence of a filter state from a previous attempt.
Externally, the user sees the exact same thing: the internet isn't working.
However, the engineering root causes are completely different.
For a proprietary VPN infrastructure, this demands separately measuring handshake success, payload transmission, reconnection behavior, route availability, and the stability of long-lived sessions.
It is especially vital to compare results across ISPs, regions, and time intervals.
Such diagnostics make it possible to distinguish between server issues and active network interference.
Why a Universal Invisible Tunnel Does Not Exist
Transport protocol developers and filtering system operators are solving opposite problems.
The former strive to ensure confidentiality, performance, and connection resilience.
The latter analyze available metadata, initial packet structures, network addresses, and flow behavior.
Consequently, any change by one side creates an incentive for adaptation by the other.
Even if a specific protocol version is not recognized by a particular filter today, it does not imply permanent invisibility.
Reliable infrastructure must be built not on the promise of eternal invulnerability for a single transport layer, but on measurements, redundancy, key protection, and the ability to correctly recover from network failures.
Main Conclusion
The history of Russian QUIC filtering demonstrates how rapidly control systems are capable of shifting from brute-force blocking of an entire protocol to analyzing specific signatures within its initial handshake.
Yet it shows something else as well.
Every complex filtering system has its own states, limitations, and implementation nuances.
These can be studied, measured, and accounted for when designing resilient networks.
Encryption protects content. Resilient architecture protects the ability to keep working. These are two distinct engineering tasks, and they must be solved together.
GLASS BRIDGE
Primary Source: Nico Heitmann, Niklas Niere, Felix Graf Lange, Juraj Somorovsky. On Russia's Early Introduction of QUIC SNI Censorship. FOCI 2026.
https://www.petsymposium.org/foci/2026/foci-2026-0010.pdf
Reproducible Research Data: