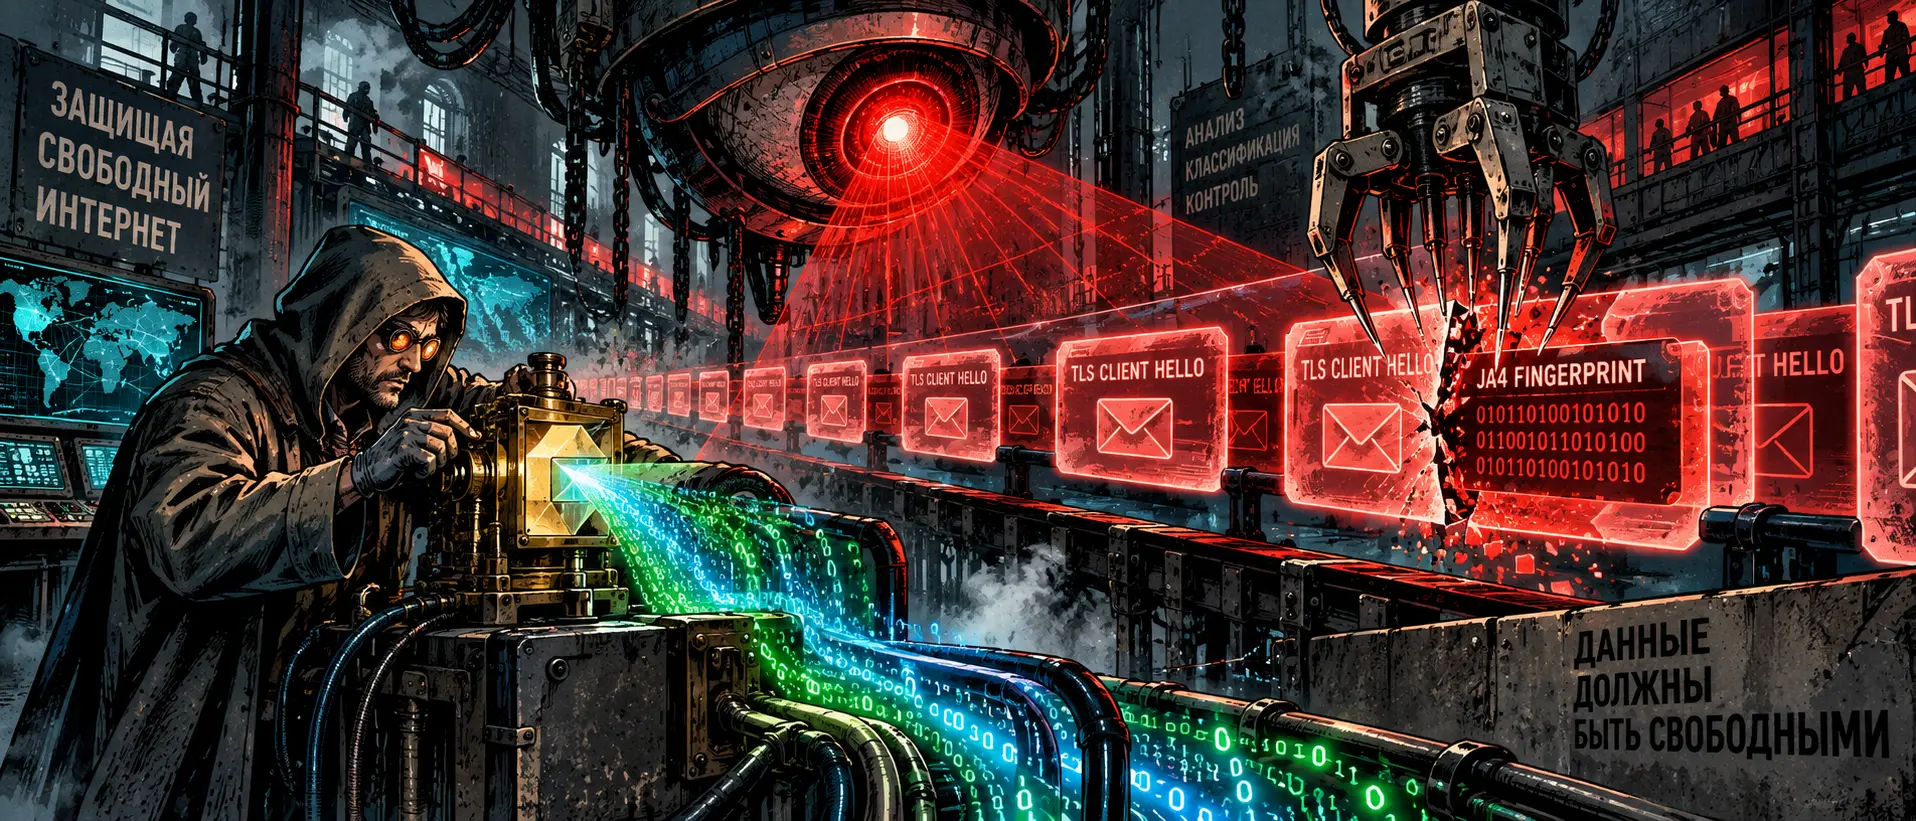
Last time, we discussed everyday deception involving 4G icons and overloaded base stations. Today, strictly following our alternating schedule, we return to hardcore engineering. A serious issue has come to a head: backbone TSPU nodes and DPI systems have begun actively rolling out next-generation handshake fingerprint analysis—the JA4/JA4+ matrices.
While node admins and private tunnel creators until recently focused on bypassing legacy signatures like JA3 (which inspected the order of ciphers and extensions in the Client Hello packet), the rules of the game have now changed. New heuristic algorithms identify non-standard clients in fractions of a second, even when the traffic is hidden behind a valid third-party TLS certificate.
For VPN operators and network security specialists, this is a challenge of an entirely different caliber.
Anatomy of a Capture: Why the JA4 Signature Sees Right Through You
Classic DPI logic was built on simple things: reading the hostname in SNI or cross-referencing the IP address with a registry. With the advent of masking protocols (VLESS Reality, Trojan), these methods were blinded. However, a client's network stack cannot be hidden by header spoofing alone:
Client Stack Fingerprinting (TLS Fingerprinting). When a legitimate browser (Chrome or Safari) initiates a secure connection, it sends a strictly defined set of supported TLS versions, compression algorithms, supported elliptic curves, and extensions in a unique order. A custom-built client or mobile core based on Xray/Sing-box generates its own profile, which is instantly flagged as "non-browser traffic."
Multidimensional JA4 Vector. Unlike the outdated JA3, the JA4 standard divides the fingerprint into logical blocks: protocol (TCP/QUIC), extension structure, supported encryption algorithms, and ALPN (Application-Layer Protocol Negotiation) signatures. If your tunnel claims to access a web server via HTTP/2, but the Client Hello lacks extensions mandatory for modern browsers (such as GREASE or ECH markers), the session is dropped via a heuristic flag.
Timings and Initial Packet Analysis (TCP Window / TCP Options). DPI analyzes TCP window parameters, the presence of selective acknowledgments (SACK), and segment size (MSS). A Linux server or modified Android client sends baseline low-level headers differently than a desktop Windows or macOS system. A mismatch between the TCP stack fingerprint and the TLS fingerprint is an instant marker of a tunnel.
Where Standard Configurations Break
Most server administrators spin up control panels with default profiles, relying on the magic of Reality. In practice, in filtering logs, this looks like this:
Freezing at the Client Hello Stage. TSPU does not block the server entirely—it simply quietly drops the connection (TCP RST) specifically for clients whose JA4 hash matches public databases of non-standard network utilities (Go clients, Python scripts, libcurl).
QUIC/HTTP3 Paralysis. Attempts to migrate to UDP transport run into even harsher filtering: unknown tokens in QUIC headers are preemptively throttled, as operator systems have learned to calculate anomalous UDP streams by entropy.
Heuristic IP Quarantine. If a series of connections with an "anomalous" TLS fingerprint toward subnets uncharacteristic of the region is recorded from a single subscriber IP address, all outgoing traffic for that client is switched to a hard throttling profile.
An Engineering Counterstrike: How to Build an Invisible Network Profile
For a node to withstand behavioral analysis systems, hiding the payload is not enough—you must reproduce the behavior of a real browser down to the last byte:
Full uTLS Stack Emulation. In client configurations, it is critical to activate mechanisms for fine-tuning the emulation of real browser fingerprints (for example, chrome_auto profiles or current Safari versions). The client must use real extension sets, including the dynamic generation of fake GREASE values to prevent hard hash-sum matches.
Using Native System Libraries. For enterprise networks and critical nodes, it is more reliable to route traffic through native operating system calls (WebSockets over a system WebView or built-in network stack), where the fingerprint is formed by the OS itself rather than a third-party compiled library.
MTU and Fragmentation Parameter Synchronization. Set packet fragmentation parameters so that the size of the first data block fits perfectly into standard browser request sizes. Breaking the Client Hello into fragments under 100 bytes confuses hardware TSPU pipelines, forcing them to pass the session without detailed comparison against signature databases.
Deep packet inspection has ceased to be theory from cybersecurity textbooks—it is the daily reality on network backbones. Today, the reliability of private infrastructure is determined not by the power of a rented server, but by the precision of network stack configuration down to the final bit.
SEO Keywords: ja4 tls fingerprint blocking, how tspu detects vpn, utls chrome emulation, client hello tls 1.3 blocking, dpi traffic analysis ja3 ja4, vless reality signature bypass configuration, network protocols cybersecurity 2026