Last time, we took a deep dive into the implementation of national certificates and how operating systems are trying to legitimize end-to-end wiretapping. Today, right on schedule, we are turning our sights to a pressing everyday issue that consistently boils the blood of virtually every smartphone user.
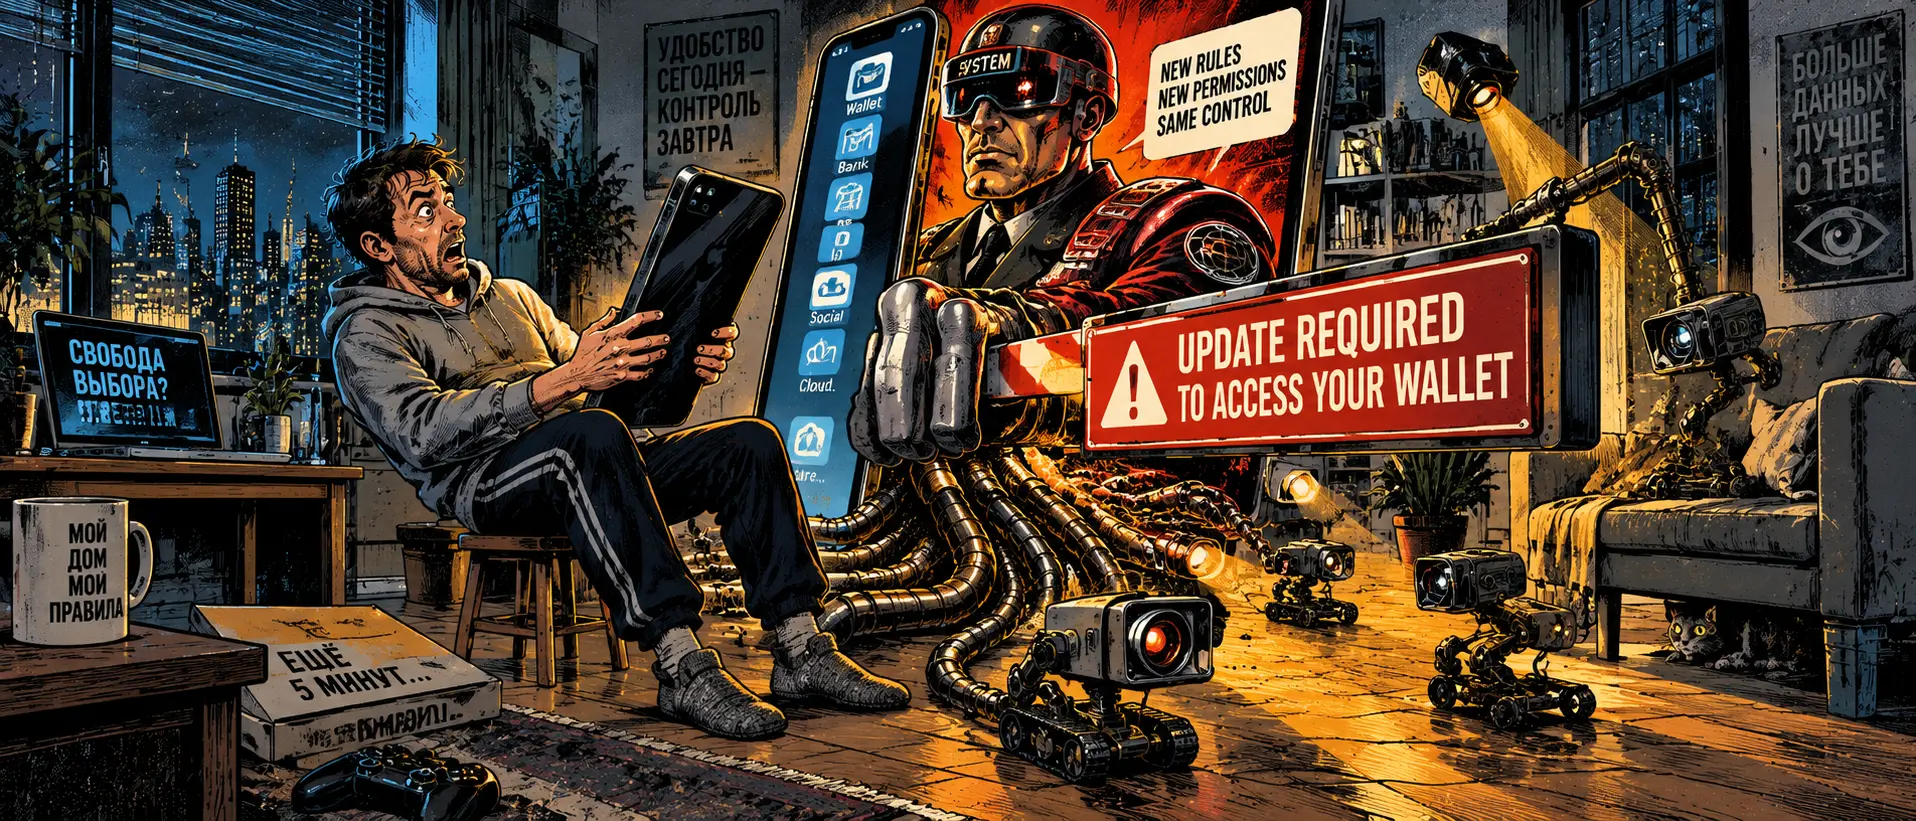
Picture this: you urgently need to transfer money, pay a tax, or pull up a digital ID at the checkout. You open the app, only to be greeted by a blank screen with an uncompromised ultimatum:
“Your app version is outdated. A mandatory update from the local app store is required to continue.”
There is simply no “Later” or “Close” button. You are grabbed by the scruff of the neck and forcibly herded into installing a fresh APK file. Fail to update, and you are left without access to your own money and documents.
Under the hood of updates: what is actually being sewn into your phone
You will always be fed the same old line about “improving stability” and “enhancing payment security.” In reality, every such ultimatum-driven update hides entirely different technical realities:
Embedding alternative SSL certificates. Foreign app stores (the App Store and Google Play) are gradually removing apps from sanctioned entities or rejecting builds with opaque code. To bypass this, developers release versions that have that very same local root certificate hardcoded right into them. The app stops trusting independent global centers and switches entirely to servicing via controlled gateways.
Aggressive anti-fraud scanners disguised as “care.” Modern versions of banking clients have long turned into full-fledged spyware-antiviruses. They scan the list of all apps installed on your device, check for root access, look to see if USB debugging is enabled, and analyze which tunnels and network utilities are running in the background. Spot a “suspicious” network profile? The app quietly limits transaction limits or blocks login altogether.
Eliminating web interfaces. Banks find it fiercely unprofitable for you to log in via a standard browser equipped with secure extensions and ad blockers. In a browser, you control the environment. Inside a closed binary app, the OS sees only what the developer permits.
The paradox of coercion: how digital security breaks
The main irony is that for years, people have been taught basic hygiene rules: “Never download files from unverified sources, and never check the box for ‘Allow installation from unknown sources.’”
And now, corporations and government agencies themselves are training millions of people to:
Visit third-party websites via links from SMS messages.
Download nameless .apk files directly into device storage.
Disable built-in Android system protection mechanisms.
This is a fundamental breakdown of user vigilance. When a grandmother or a student is taught to blindly tap “Allow installation from this source” just to access a pension account or scholarship, next time a real banking Trojan arrives via the exact same route, the person won't even notice the difference.
Network self-defense: how to keep services from digging deeper than necessary
If you cannot avoid using intrusive software, here are a few working isolation practices:
Use Progressive Web Apps (PWAs). Most sensible services support mobile web versions that can be added to your home screen as a shortcut. Inside the browser container, the site has no direct access to your file system, the phone's process list, or background network services.
An isolated Work Profile (Work Profile / Shelter). On Android, use isolated environments like a work sandbox. All demanding banking apps, marketplaces, and government services should live there. This isolated profile has no access to your primary contacts, family photos, or private utilities.
Split tunneling. Configure your network tunnel so that finicky local financial updates go directly through your cellular carrier, while all your browser traffic, work messengers, and system browsing go through a reliable, encrypted external channel. This will eliminate constant false alarms from banking anti-fraud systems.
Security isn't about someone twisting your arm with another mandatory update—it's about you deciding which doors on your smartphone stay locked.