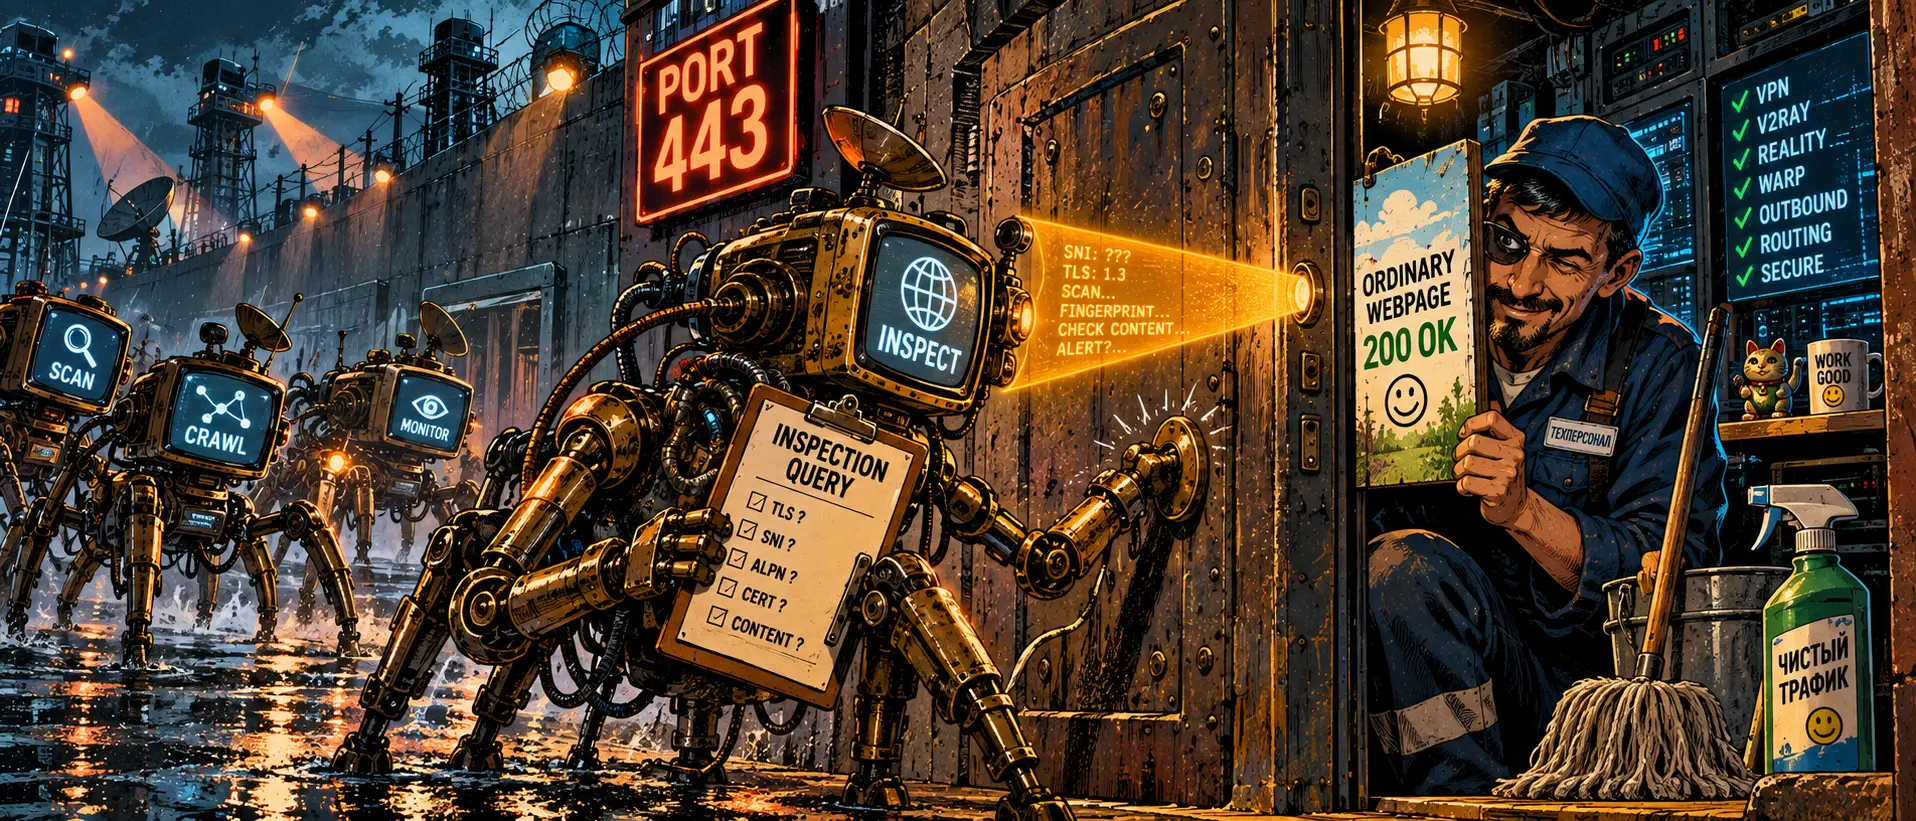
Last time, we dissected the hype surrounding the Ministry of Industry and Trade's scrap disposal fee and how public channels farm engagement using the word "tax." Today, strictly following our alternating schedule of "everyday pain vs. engineering hardcore," we are returning to the level of bytes, sockets, and network routing.
Let's talk about a hidden threat faced by anyone who sets up their own gateway or maintains a node infrastructure: the mechanics of active probing.
The symptom is familiar to any observant admin: you spin up a server, configure a fresh obfuscation protocol, bind a domain, and connect two or three clients. The logs are clean, the load is minimal, and DPI rules seem to have been bypassed. But anywhere from two hours to a couple of days later, the node's IP address suddenly stops responding to incoming handshakes from inside the filtration perimeter. Meanwhile, from any other point on the globe, port 443 remains open and accessible.
You weren't "caught by traffic volumes." Someone simply came to visit you with a secret audit.
Anatomy of an Active Probe: How a Network Provocateur Works
When a TSPU system on the backbone spots a session to a foreign IP address that its heuristic filters cannot unambiguously classify (no open SNI from the whitelist, an atypical encryption profile, suspicious entropy), it doesn't risk cutting the connection right away—doing so risks false positives on legitimate B2B traffic.
Instead, an active verification protocol is triggered:
On-the-fly inspection followed by a trigger. The client session is allowed to pass, but the metadata (server IP, port, timings) is instantly transmitted to a distributed network of probing scanners located within the operators' infrastructure.
Synthetic requests (Mutated Handshakes). Within seconds or minutes of your session closing, a series of specific packets arrives at your server from regulator-controlled IP addresses. This isn't just a standard nmap port scan. The probe sends:
Replay Attack: Exact byte copies of your client's first packet with minimal mutations.
Damaged TLS Client Hello: Requests with intentionally broken cipher orders or truncated extension fields.
Garbage Probing: Random byte packets sent into an open TLS socket to check the application's reaction.
Behavioral matrix matching. A real Nginx, Apache, or Caddy server receiving garbage on an HTTPS port reacts strictly according to the RFC specification: it returns a standardized error (e.g., 400 Bad Request with the code "The plain HTTP request was sent to HTTPS port") or neatly closes the session with a TLS Encrypted Alert packet bearing the decode_error code. If your proxy server simply drops the TCP session quietly via RST, times out, or responds with a non-standard packet, the probe flags an anomaly. The node is marked as an unauthorized tunnel and blacklisted.
Where the Typical Admin Setup Fails
Most online tutorials suggest setting up a so-called fallback (routing invalid traffic to a local stub site or third-party domain). But the devil is in the implementation details:
Certificate discrepancies. If a proxy accepts an incoming connection, decrypts the header, and only then decides where to redirect it, a probe with a corrupted handshake might spot a certificate fingerprint that doesn't match the public host you are mimicking.
Latency Delta. If an invalid request is forwarded to an external cover site, the probe measures the time between sending the packet and receiving a TCP RST or error response. A latency of 80–120 milliseconds immediately gives away the presence of an intermediate proxy layer.
Lack of response to HTTP methods. Probes often send classic GET / or POST methods over plain HTTP without TLS. If port 443 cannot adequately handle open HTTP requests and return a correct 301 Moved Permanently redirect, the server gets exposed during basic verification.
The Engineering Counter-Strike: Building an Impregnable Node
To withstand active probe attacks, a server must become indistinguishable from a monolithic, legitimate web server:
Local web server with a single socket (Real Fallback to Nginx/Caddy). The cover server shouldn't reside somewhere on the other end of the internet. A real web server with a valid site tied to a local socket (127.0.0.1:8443 or a unix socket) must run on the exact same machine. Any traffic that fails protocol authorization key validation must be transparently and instantaneously passed to the local Nginx, which will serve the probe an entirely legitimate response from a real website.
Tarpitting suspicious sessions (SYN Tarpit / Delay Defense). If a series of repeated handshakes without payload transmission is recorded from a single IP (a signature probing tactic), do not drop the connection via RST. Configure your firewall (iptables / nftables) to hold the socket in limbo with a minimal receive window (TCP Zero Window). The probing scanner will exhaust its thread limit and move on to check other targets.
Blocking known scanner Autonomous Systems. A significant portion of probes are launched from fixed address ranges belonging to research institutes, operator gateways, and monitoring data centers. Geo- and ASN-filtering at the firewall level, blocking suspicious scanning subnets from direct access to port 443, cuts off up to 85% of synthetic checks before they even touch the TLS stack.
Modern censorship no longer features passive observers: every closed channel is watched by algorithms ready to knock on your door with an audit. And the only node that survives is the one that knows how to open that door wearing the face of a boring, unremarkable web server.
Keywords (SEO): active probing dpi tspu, active probing bypass blocks, configuring fallback xray vless, why vps server ip gets blocked, replay attack vpn blocks, protecting node from port scanning, tunnel network security 2026