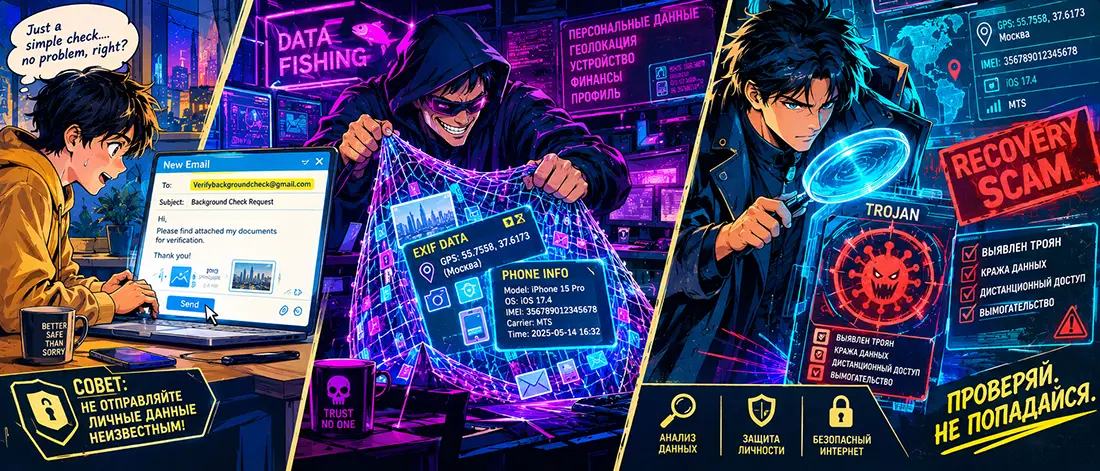
One of the most insidious techniques in modern social engineering is the so-called "secondary scam" (Recovery & Verification Scam). When a user is already frightened by news about data breaches, hacks, or romance fraudsters, they lower their guard the moment someone extends a "helping hand."
A striking example recently surfaced on the popular platform Quora in a thread fittingly named reportscam. The article begins with classic, sound advice on how to spot romance scammers: manipulation, early declarations of love, and attempts to move the conversation off the platform. But in the very final paragraph, the author inserts a recommendation that invalidates everything:
“Save a copy of their profile picture, and then send it to Verifybackgroundcheck@gmail.com for verification...”
This is a textbook example of how a basic security article turns into a tool for harvesting digital footprints and compromising the user.
1. Anatomy of a Trap: Why Scammers Want Your "Verification"
Why is an ordinary free mailbox on @gmail.com provided instead of a link to a legitimate search service or official verification tool?
- Lead Qualification.
- A person who sends someone else's photo to such an address is directly tipping off attackers with key intelligence: "I am actively looking on dating sites, I am emotionally invested, but I have doubts." In the database of social engineering, such a contact immediately gets top priority—the victim is already vulnerable.
- Dossier Enrichment and Metadata Leakage.
- The user's real e-mail is sent along with the message. If the photo is transmitted as an original file (without prior stripping), scammers obtain EXIF data: smartphone model, exact GPS shooting coordinates, and timestamps.
- Extortion for a "Paid Report" or Infection.
- In a reply email, the victim is typically told: “Yes, this person was found in a database of dangerous criminals/fraudsters. To get the full dossier with evidence, pay a $30–50 fee.” In a worst-case scenario, an archive or "secure PDF report" containing a Trojan designed to intercept sessions and crypto wallets is attached to the email.
2. Technical Evolution: Why Old Advice No Longer Works
The Quora text clearly demonstrates the crisis of classical security advice. What worked in 2018 is useless today:
- Reverse Image Search is Outdated.
- Modern syndicates do not use stock photos or pictures of real Instagram models—they are too easy to find. Faces are generated by neural networks in a single click. Such an image has no duplicates on the internet: a reverse search via Google or TinEye will return zero matches, creating a false illusion for the user that they are dealing with a "real person."
- Video Calls Are No Longer an Absolute Guarantee.
- The implementation of real-time deepfake models allows attackers to overlay someone else's appearance and synthesize a voice right in the call window. The only way to break through a software filter is unconventional dynamics: asking the interlocutor to quickly pass their hand in front of their nose or turn their head 90 degrees. Neural network masks instantly glitch and distort during such movements.
3. Where the Bait-and-Switch Happens: Account Hacking vs. Social Engineering
The original article's headline claims to cover: “How do scammers gain access to your account?” But the body contains not a single word about tokens, session cookies, credential phishing, or the interception of SMS codes.
Instead, it describes psychological blackmail. This is a frequent trick used by authors of such content: exploiting the fear of technical hacking to sell a primitive trust-based scam scheme.
Real account hacking on platforms happens differently:
- via fake login pages (OAuth phishing);
- via malicious browser extensions that steal saved sessions;
- via database leaks followed by Credential Stuffing attacks.
Summary: Rules of Digital Hygiene
- Never send data to "service" addresses of free email services. No legitimate security service, anti-fraud laboratory, or verification platform accepts requests via
@gmail.com,@yahoo.comor@mail.ru. - Use standalone local tools. Metadata verification, EXIF scrubbing, and visual searches should be performed through trusted search platforms or local software, not through shady intermediaries.
- Maintain Skepticism Toward Open-Posting Platforms. Any open Q&A base (Quora, Reddit, niche forums) is flooded today with hidden spam, where a useful introductory section is written solely to push a malicious contact in the final paragraph.
Security begins with critical thinking: if the advisor themselves asks you to send them your files and emails, you are not looking at protection, but at the next stage of an attack.